Contextual data security specialists
Know where your data lives. Control where it goes.
We evolve traditional Data Loss Prevention (DLP) into Contextual Data Security (CDS), protecting your enterprise from prompt-based exposure, shadow AI, and generative data exfiltration while keeping your business moving.
Cost-flexible, milestone-based engagements with clearly defined deliverables
- Federal government
- State & local
- Healthcare
- Finance
- Legal
- Education
- Entertainment
The visibility problem
Most organizations don't have a data problem. They have a visibility problem.
Sensitive data moves through email, endpoints, cloud shares, and collaboration tools faster than most security teams can inventory it. Traditional DLP tools block what they can pattern-match, but they cannot interpret intent, context, or the new exfiltration paths generative AI has opened. Contextual Data Security closes that gap with controls built on a defensible understanding of what data you hold, where it lives, and how it legitimately flows.
- A defensible inventory of sensitive data is the foundation for every contextual control we build.
- We monitor first and enforce later, so protection is tuned to your real business workflows.
- Risk is baselined at the start and re-measured at a defined interval (for example, 90 days).
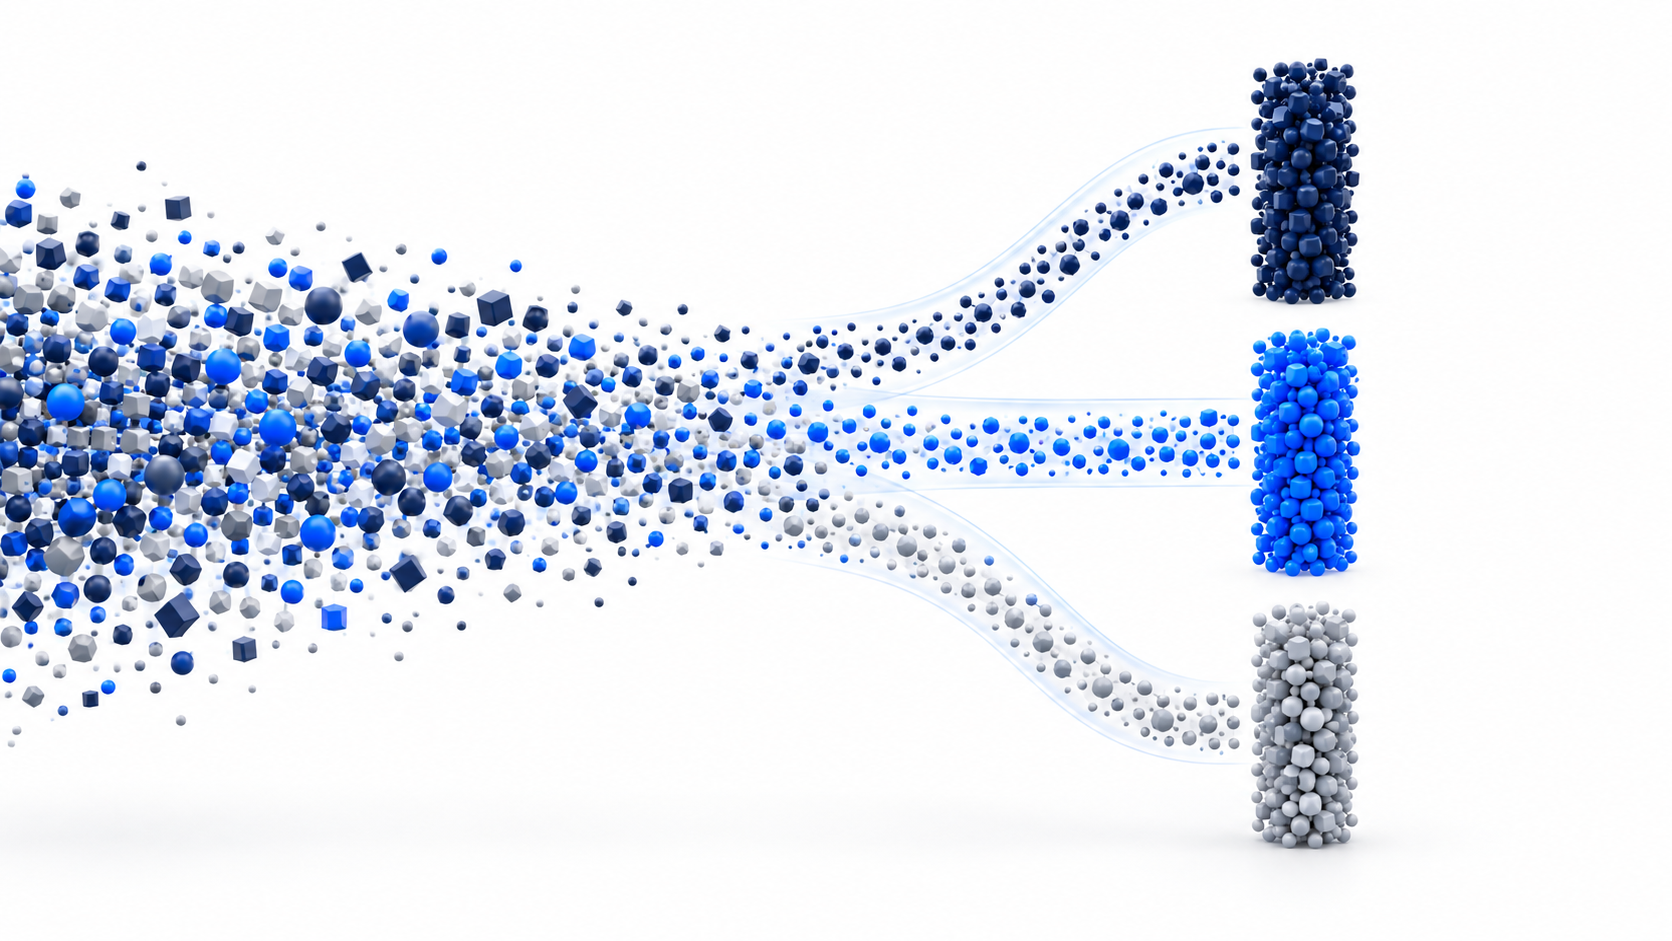
The Three Pillars of CDS
Our services framework: three pillars, one continuous data perimeter.
Our consulting offerings are grouped into clear, logical pillars that show how we implement Contextual Data Security, from the AI frontier to your internal core to the legacy foundation beneath it all.
Guarding the Frontier
GenAI exfiltration & prompt security. We secure the interactions between your workforce and external public AI models: inline prompt redaction, shadow AI discovery, and multi-turn contextual analysis.
Pillar 2Securing the Core
Internal AI & agentic RAG governance. We protect your internal data repositories from being weaponized by your own AI deployments through data lineage mapping, over-permissioning remediation, and injection defense.
Pillar 3Evolving the Legacy Foundation
Modernized DLP integration. We don't abandon your compliance investments; we supercharge them with hybrid architecture, behavioral policy engines, and DDR playbooks.
Six-point service coverage
Every layer of data protection, one team.
The pillars are backed by our proprietary six-point security brief covering the full scope of data security, so nothing falls between vendors, tools, and teams.
 01
Data Loss Prevention
Enterprise DLP platforms: policies, custom identifiers and endpoint rollout.
 02
Discovery & Classification
Know what you hold with a defensible sensitive-data inventory.
 03
Encryption & Key Management
Lost devices and misdirected email become non-events.
 04
Identity & Access Management
Right people, right access. Nothing more.
 05
Governance & Compliance
Audit-ready evidence for HIPAA, GDPR and more.
 06
Cloud & Endpoint Protection
One standard of protection across cloud, endpoint and on-prem.
Our methodology
A proven, phased path from visibility to enforcement.
Used with mid-size to large enterprise customers, from initial planning through steady-state monitoring and enforcement.
 Phase 1
Planning
Kickoff, scope and business requirements.
 Phase 2
Technical Assessment
Licensing, policies, roles and incident response reviewed.
 Phase 3
Modification
Settings, discovery and custom data identifiers configured.
 Phase 4
Monitor
Best-practice policies run silently, with no user alerts yet.
 Phase 5
Notification
Policies tuned by severity; employee notices switched on.
 Phase 6
Block / Enforce
Final tuning, then automated blocking goes live.
Measurable risk reduction
Risk goes down in stages, and we prove it.
In parallel with the project methodology, we apply a four-stage model that reduces risk measurably over time, with an initial baseline re-measured after a defined interval such as 90 days.
Why Triple 5 Defense
Certified specialists. National-scale experience.
Start with visibility
Ready to see where your data is going?
Book a scoping call. We'll review your current data security posture, licensing, and data flows, then outline what a phased engagement would look like for your environment.